
Entering an online casino account in Poland has evolved far beyond a simple username and password. Sites such as Pinco Casino now provide a range of authentication mechanisms designed to reconcile user convenience with stringent security requirements. The login page acts as the critical gateway where identity verification, data encryption, and regulatory compliance come together. For Polish players, grasping these methods is not just about ease of entry; it is about securing personal information and funds in a market controlled by the Ministry of Finance and the amended Gambling Act. Each login technique carries distinct technical implications, from session token management to multi-layered credential checks, and a clear grasp of these options empowers users to make informed choices about their digital safety.
Social Media and SSO Connections
SSO enables Polish players to enter Pinco Casino using existing credentials from trusted third-party providers such as Google or Facebook. This method transfers authentication to an external identity provider, which issues a token confirming the user’s identity without sharing the actual password with the casino platform. The technical backbone is commonly OAuth 2.0 or OpenID Connect, protocols that provide limited access scopes. For the user, this eradicates the need to remember another password and speeds up the login process significantly. However, it also connects the casino account’s security to the integrity of the social media account. If the Google or Facebook profile is compromised, the attacker could conceivably gain entry to the linked Pinco Casino account, making the protection of that primary account critically important.
Associating Accounts Safely
When a Polish player decides to connect a social account to Pinco Casino, the platform starts a redirect to the provider’s authorization server. The user authenticates there and gives consent for Pinco Casino to retrieve basic profile information. The casino does not see the social media password; it obtains an access token and a refresh token. To ensure security, players should check the permissions requested and make sure they are comfortable with the data being shared. It is also recommended to turn on two-factor authentication on the social media account itself, creating a layered defense. In the event of a token compromise, the damage is restricted because tokens have short lifespans and can be revoked from the provider’s security dashboard without influencing other services.
Data Protection Considerations
Employing social login introduces specific privacy concerns under the European General Data Protection Regulation, which applies fully in Poland. Pinco Casino must clearly reveal what personal data it receives from the identity provider and how that data is processed. Usually, only the email address, name, and profile picture are shared, but users should review the privacy policy. The casino does not get access to friend lists or private messages. Polish data protection law, upheld by the Urząd Ochrony Danych Osobowych, grants players the right to request deletion of this data. Opting for social login can decrease the amount of personal information held directly on the casino’s servers, as the authentication burden transfers to a third party with dedicated security teams.
KYC Verification and Regulatory Compliance in Poland
Before any sign-in method grants complete access to withdrawals and full gameplay, local regulations mandates a KYC process. Pinco Casino must verify the identity, age, and address of each player to satisfy anti-money laundering regulations and the Polish Gambling Act. This verification is directly connected with the login system; an account may be opened and accessed, but its capabilities remains limited until the KYC checks are finished. The process commonly entails uploading a scan of a official identification document, a proof of address document, and at times a selfie for liveness detection. Once verified, the account status is irreversibly connected to the login credentials, and any later modification in personal details initiates a re-verification workflow.
Document Upload and ID Verification
During the registration flow at Pinco Casino, Polish players are asked to submit a clear image of their dowód osobisty or passport. The platform utilizes automated optical character recognition to extract the name, date of birth, and document number, cross-referencing this data against sanctions lists and PEP databases. Manual review by a compliance team follows if the automated check flags any discrepancy. The uploaded documents are encrypted at rest and transmitted over TLS, assuring that sensitive personal data is kept protected. Players should make sure the images are well-lit and all corners of the document are visible to avoid delays. A successful identity check permanently links the verified identity to the login account, preventing duplicate or fraudulent registrations.
Address Verification and Payment Method Validation
To fully activate a Pinco Casino account, proof of residential address in Poland is required. Approved documents consist of a latest utility bill, bank statement, or official correspondence showing the player’s name and address, dated within the last three months. This step confirms the player’s jurisdiction and tax residency. Additionally, when a payment method like a credit card or e-wallet is linked, the casino can require a photo of the card with certain digits obscured or a screenshot of the e-wallet profile. This verification connects the financial instrument to the verified identity, blocking money laundering. Only once these checks are completed does the login offer full transactional privileges, a process that usually finishes within twenty-four hours.
Traditional Email and Password Authentication
The email and password combination remains the most popular login method across Polish casino platforms, like Pinco Casino. This approach is based on a registered email address serving as the unique identifier, combined with a secret passphrase known only to the user. The server stores a salted hash of the password, never ever the plain text, and compares the submitted credential against this hash during each login attempt. While familiar, this method’s security depends heavily on the strength of the chosen password and the user’s diligence in avoiding reuse of credentials across multiple services. Polish players need to know that brute-force attacks and credential stuffing are constant threats, making it vital to grasp how to reinforce this basic authentication layer.
Establishing a Strong Password
A strong password for a Pinco Casino account must surpass twelve characters and mix uppercase letters, lowercase letters, numbers, and special symbols in an unpredictable sequence. Refrain from using dictionary words, personal dates, or simple patterns such as “Warszawa123!” which attackers can break within seconds using hybrid dictionary attacks. Password managers create and store complex strings, lifting the cognitive burden from the user while ensuring each service has a separate credential. The login system at Pinco Casino imposes minimum complexity requirements and may refuse passwords that appear in known breach databases. Polish users who create a truly random passphrase significantly lower the risk of unauthorized access, as the time required to brute-force a long, high-entropy password reaches into centuries with current computing power.
The Function of Email Verification
Email verification functions as an initial barrier during the creation of a profile at Pinco Casino. Once you submit the enrollment form, the platform sends a temporary, non-reusable verification link to the supplied email. This step verifies that the player controls the mailbox and establishes a trustworthy line of communication for subsequent safety messages. In Poland, where email providers like Onet, WP, and Gmail are common, users should verify their spam filters do not prevent these critical messages. The validation token is cryptographically signed and has a short lifespan, preventing replay attacks. Once confirmed, the email address serves as the cornerstone for password recovery and critical account notifications, making it a fundamental part of the entire login ecosystem.
Security Best Practices for Casino Authentication
Beyond the various login methods offered by Pinco Casino, Polish players should implement a set of security measures that protect their accounts from common threats. The human factor stays the weakest link in any authentication chain, and social engineering attacks particularly aim at users who may not recognize the warning signs. Using unique passwords, enabling all available 2FA options, and monitoring account activity regularly make up the foundation of a secure gaming experience. Players should also be conscious of the devices and networks they use to log in, avoiding public Wi-Fi without a VPN. A proactive stance on security guarantees that the technical safeguards built into the casino’s login system function as intended without being undermined by careless behavior.
Identifying Phishing Scams
Phishing campaigns targeting Polish casino players often involve emails or SMS messages that copy official Pinco Casino communications, urging recipients to click a link and log in. These fraudulent pages are designed to capture credentials and 2FA codes in real time. Legitimate casino messages will never ask for a password or a one-time code via email. Players should always check the URL in the browser address bar, ensuring it begins with the correct domain and displays a valid TLS certificate. Bookmarking the official login page and using it exclusively removes the risk of following a malicious link. Reporting suspicious messages to the casino’s security team helps protect the wider community and allows the platform to take down phishing infrastructure quickly.
Handling Session Timeouts and Device Recognition
Pinco Casino employs session management features that automatically log out inactive users after a period of idleness, minimizing the window of opportunity for unauthorized access on shared or unattended devices. The “remember this device” option places a persistent cookie that skips 2FA on subsequent logins from the same browser, swapping some security for convenience. Polish players should only activate this feature on personal, password-protected devices. Clearing browser cookies periodically neutralizes these remembered tokens and forces a full re-authentication. If a device is lost or stolen, the account dashboard provides an option to remotely terminate all active sessions, instantly logging out any device that may have been compromised and securing the account balance.
Bezheslové Způsoby autentizace
The move směrem k passwordless authentication nabírá traction, přičemž Pinco Casino supports methods které ruší pevné password zcela. Tyto techniky závisí na základě possession-based factors nebo biometrics alone, omezující friction and removing the risk znovupoužití hesla. Kouzelné odkazy a one-time passcodes sent to a verified email či phone number allow uživateli klepnout na odkaz nebo enter a code to gain instant access. Hardwarové bezpečnostní klíče poskytují another path, používající physical devices jež přenášejí data via USB či NFC. For Polish players znechuceným by forgotten passwords, passwordless login poskytuje plynulý experience bez compromising security. Základní cryptography garantuje that každé přihlášení je unikátně autentizováno and cannot be replayed, což z něj činí budoucnostní solution.
Magické odkazy a Jednorázové kódy
Magický odkaz is jedinečnou, time-limited URL sent na hráčovy registered email address. Jeho rozkliknutím autentizuje relaci rovnou without requiring heslo. Pinco Casino generuje these links s kryptografickým nonce a nastavuje an expiration window of a few minutes. Stejně tak, a one-time passcode delivered přes email nebo SMS lze napsat do přihlašovací formulář. Obě metody verify vlastnictví nad komunikačním kanálem. Polští hráči by měli mít na paměti that the security tohoto přístupu se přesouvá to the email or phone account; pokud je tato schránka napadena, útočník může požádat kouzelný link a získat přístup. Z tohoto důvodu, ochrana přidruženého e-mailu silným silným heslem a dvoufaktorovou autentizací zůstává nezbytné i když používáte passwordless casino login.
Hardwarové bezpečnostní klíče
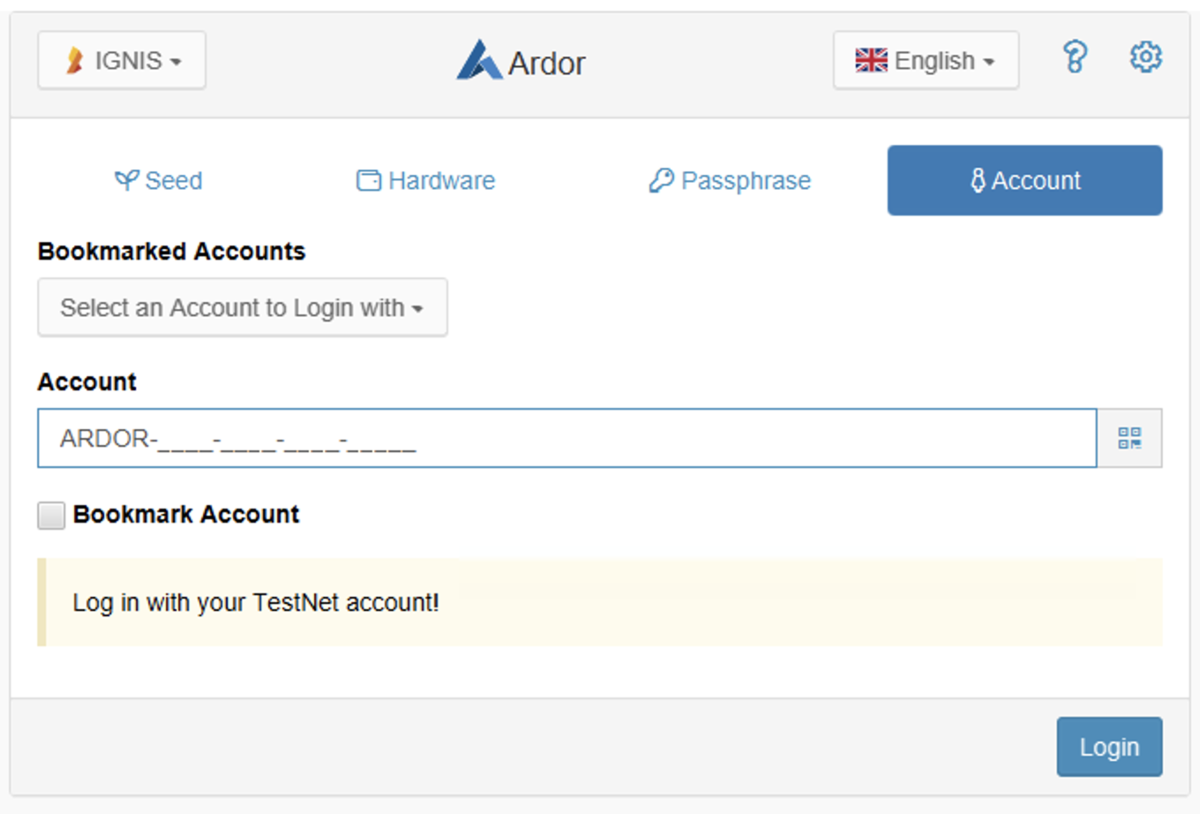
Hardware security keys kompatibilní normám FIDO2 a U2F standards jsou vrchol autentizace odolné vůči phishingu. A Polish player může registrovat a physical key, such as YubiKey, with svého online kasyno pinco logowanie do Casino účtu. Během přihlašování, the platform challenges the key, which requires fyzické stisknutí to generate kryptografické signatury. Klíč uchovává a private key jenž nikdy neopustí zařízení, and each response je vázána na konkrétní doménu, zabraňující man-in-the-middle attacks. Dokonce i sofistikovaná phishing site mimicking Pinco Casino nedokáže přimět the key into responding. I když tato metoda vyžaduje purchasing a device a jeho nošení, přínosy pro zabezpečení are substantial pro cenné účty. Přihlašovací rozhraní kasina umožňuje více klíčů jako zálohy, zajišťující, že přístup zůstane možný pokud je jeden klíč ztracen.
Dual-Factor Authentication and MFA
Two-factor authentication adds a essential extra layer past the passcode, necessitating a knowledge factor and what the user has. For Pinco Casino, turning on 2FA signifies that should a attacker gets the correct password, they are unable to log in absent the secondary factor. This greatly decreases the efficacy of phishing and identity theft. The most frequent deployments use TOTP codes produced by an authentication app or sent via SMS. Multi-factor authentication can broaden this to include biometric inherence factors. Regarding Polish players who maintain a account balance or possess payment methods connected, turning on 2FA represents one of the most impactful steps to stop unapproved transactions and account theft, converting the login process into a robust security gate.
SMS-based and 2FA App Codes
SMS 2FA sends a digital code to the user’s registered mobile phone number, which must be entered on the Pinco Casino login page. While better than no second factor, SMS codes are vulnerable to SIM swapping attacks and interception. A more secure alternative is a specialized authenticator application such as Google Authenticator or Authy, which generates codes locally on the device using a shared secret and the current time. These codes update every thirty seconds and are independent of the mobile network. Polish users ought to store backup codes in a safe place when setting up app-based 2FA, as misplacing the device without a recovery method can block them from the account. The casino supplies these one-time recovery keys during the initial setup wizard.
Biometric Identity Check on Mobile Devices
Modern smartphones popular in Poland offer fingerprint scanners and facial recognition systems that can serve as a biometric factor for casino logins. Pinco Casino’s mobile platform can integrate with the device’s native biometric APIs, allowing a player to authenticate with a touch or a glance after the initial password entry. The biometric data itself never leaves the device; the phone simply confirms a match to the stored template and sends a signed assertion to the app. This method provides high convenience and strong security, as biometrics are extremely difficult to replicate. However, it is tied to the specific hardware, and a factory reset will require re-enrollment. Biometric login works best as part of a multi-factor strategy rather than a standalone replacement for a password.
Logging into Pinco Casino
Pinco Casino has designed its login interface to guide Polish users through a smooth and safe entry process. From the initial registration form to the post-login dashboard, every step is created with clarity and compliance as a priority. The page adapts to the user’s device, delivering a responsive layout that performs equally on computers and mobile devices. Error messages are specific and helpful, specifying if a password is invalid or an account is locked after several failed attempts, without revealing whether the email address exists in the system. This attention to detail reduces frustration while maintaining a defensive posture against enumeration attacks. The whole process is available in Polish, guaranteeing that Polish speakers face no language obstacles during essential security steps.
Registration and Initial Login Process
New players at Pinco Casino starts by clicking the registration button, which opens a form asking for an email address, a password, and personal details like full name and date of birth. After accepting the terms and conditions and verifying they are over eighteen, the system sends the email verification link. Clicking it finishes the initial setup, and the player can log in immediately with the chosen credentials. The first login activates a prompt to set up two-factor authentication, although this may be postponed. The interface then directs the user to the KYC upload section, where identity documents may be uploaded. This sequential flow ensures that no step is overlooked, and the account status is clearly shown on the dashboard at all times.
Account Recovery and User Assistance
If a Polish player forgets their password or loses access to their 2FA device, Pinco Casino offers a structured recovery path. The “forgot password” link triggers an email with a reset token that is usable for a short period. For lost 2FA devices, the player must contact customer support and go through a manual identity verification process, which can involve answering security questions and submitting a photo holding their ID. The support team, offered in Polish, evaluates each case individually to prevent social engineering attacks. Once identity is established, the 2FA is reset, and the player can register a new device. This equilibrium between self-service recovery and human intervention guarantees that legitimate users regain access without creating a loophole for attackers.
